Showing posts with label online. Show all posts

Wednesday, April 19, 2017

How to Protect Your Credit Card Online

In this day and age, the only way to be sure that your credit card is safe is to, not have one.  Of course, the practical consequence of not having a credit card means no online shopping, no convenient on the go purchases and no easy digital management of various expenses.

Even mobile payments are tied to credit cards with precious few options to avoid the ubiquitous payment method.

Since not having a credit card is not practical (for me at least), let’s look at some tips to add security in an unsure cyber world.

Do Use Secure Sites with HTTPS 

It goes without saying that you should only share your credit card information with trusted sites, but how do you know you can trust the site.  Well, one thing to look out for is a little lock icon in your browser representing the HTTPS; the ’s’ stands for secure (the HTTP means Hypertext Transfer Protocol if your interested).  Traffic on sites designated with the HTTPS is encrypted.

Reputable shopping sites like Amazon and even smaller shopping sites can make use of encryption to add another layer of protection to your personal financial information.  If, it ain’t got the ’s’, don’t drop the $.  Simple.

Do Monitor Statements 

Online shopping is so convenient.  So too, is checking your statement online.  And the two should never be separated.  Continuous monitoring of your transactions with a view to quickly identify and immediately report suspicious charges is a requirement of responsible online shopping practices.

If you consider even that too much, automate the process.  Have your credit card company text you after ever transaction and report any fraudulent transactions faster than a Lamborghini can do zero to 60 mph.

Do Use Unique Passwords

Sure.  It can be a pain to use a different password for every site.  But, it is necessary.  Even reputable businesses can be compromised putting your other accounts in danger.  Unique passwords can help stop hackers in their tracks and keep their nefarious actions at bay.

Develop a system to help you remember the passwords or use a password manager like 1Password or LastPass.  If you’re a Mac, consider the free, built-in, seamless iCloud KeyChain.

Regardless of which system you use, do immediately, if not already done, upgrade to two-factor authentication (2FA) on every account that offers the option.  2FA also adds an extra layer of security; in many cases when logging in, users have to enter a code issued via a text, an app or dedicated device, in addition to the correct password.


Do Secure Your Network

That “free” hotspot is tempting.  But nothing in life is truly free.  Many ask you to register your email address and then hit you with spam.  Some are not secure, deliberately or accidentally.  Tempting as it may be, use secure mobile data, a Wi-Fi analyzer to assess the network or a VPN (Virtual Private Network) to “scramble” your internet signals.

If you must jump on to a hotspot unprotected, avoid open networks (no password requirement), check with the proprietor to ensure the SSID is not being spoofed, light up a firewall, and limit your online traffic to the essentials.

Make sure your system OS (Operating System), software, apps, anti-virus and anti-malware are all up to date.

Do Consider Alternatives

PayPal and similar services put ‘distance’ between your credit card and the merchant.  Many credit card companies offer excellent alternatives like ‘disposable’ card numbers and secondary PIN verification for transactions.

Don’t Email/IM Credit Card Info

This advice has been repeated over and over and over again.  Yet we keep doing it.  Never, never send your credit card number, expiration date and/or CIS, your PIN or your password via an email message or instant message (IM).

Even if you think your email account is impenetrable (and it is not), the recipient's account could be compromised leaving you exposed.  It is just not worth it.

Don’t Auto Complete Card Numbers

Browsers, under the guise of being helpful, offer to auto-complete forms.  It’s a great idea for when you type your name, not so much when typing your credit card information.  Consider turning off this feature for all sensitive financial data and key in the numbers yourself.

In that same vein, don’t store your card information on the site.  Many sites encourage you to create accounts (with your card information) to make future transactions easier.  Don’t trade ease for security and opt, where possible, not to permanently hand over your account digits.

Don’t Respond to Suspect Email

This one is hard.  Phishing emails are becoming more sophisticated and more difficult to spot.  The email may appear to come from your bank, or your boss or your spouse and ask you to verify your information by clicking on a link.  There are countless other scenarios that appear legitimate but are not.  Don't assume the sender is who they say they are just because they have some information.

The bottom line, be VERY careful.  Pick up the phone and call your financial institution, go directly to the official website and avoid clicking on the link, update your virus protection systems, never auto download attachments and be very suspicious of almost everything.  Paranoid much?  Perhaps.  Protected? Definitely.

Don’t Withdraw Cash Unnecessarily

Aside from being hit with high fees for each withdrawal, you have to watch out for skimmers on ATMs, so the fewer trips to the ATM, the better.

Try to withdraw a little more cash than you immediately need, use your smartphone to make a video recording of the transaction, photograph and keep your receipt, only use well-lit ATM in high traffic/well-populated areas and inspect that machine before and after use.  This, along with vigilant monitoring of your online statements, should help reduce the incidences of fraud.

Sources:
Daily Telegraph
Bank of America

Tech4Life airs on @RJR94FM every Tuesday morning at 8:15 am

Thursday, April 6, 2017

How to Spot Fake News

Sadly, fake news is not new; it’s just topical.

The internet has morphed what we once knew as propaganda into what we now call fake news by reducing the cost, time and possible litigation related to creating and disseminating intentionally deceptive, biased or blurred truth stories.  Wow; that was a lot to say.  Fake news is, after all, a complicated affair.

For this discussion, I am not including deliberate and obvious satire like The Onion, but rather the divisive, intentionally misleading and potentially destructive lies masquerading as genuine news.  

The growing problem of fake news proliferation is exacerbated by “the filter bubble”.  Popular (social) media sites often employ algorithms to retain visitor interest by prominently posting content we like and burying posts we don’t.  We are therefore responsible for our own “truth filter”.

We must employ our own “truth filter” and halt the spread of fake news.  Excuses like, “I’m just passing it on as I get it” and "I'm not sure its true but sharing anyway," are just plain irresponsible.

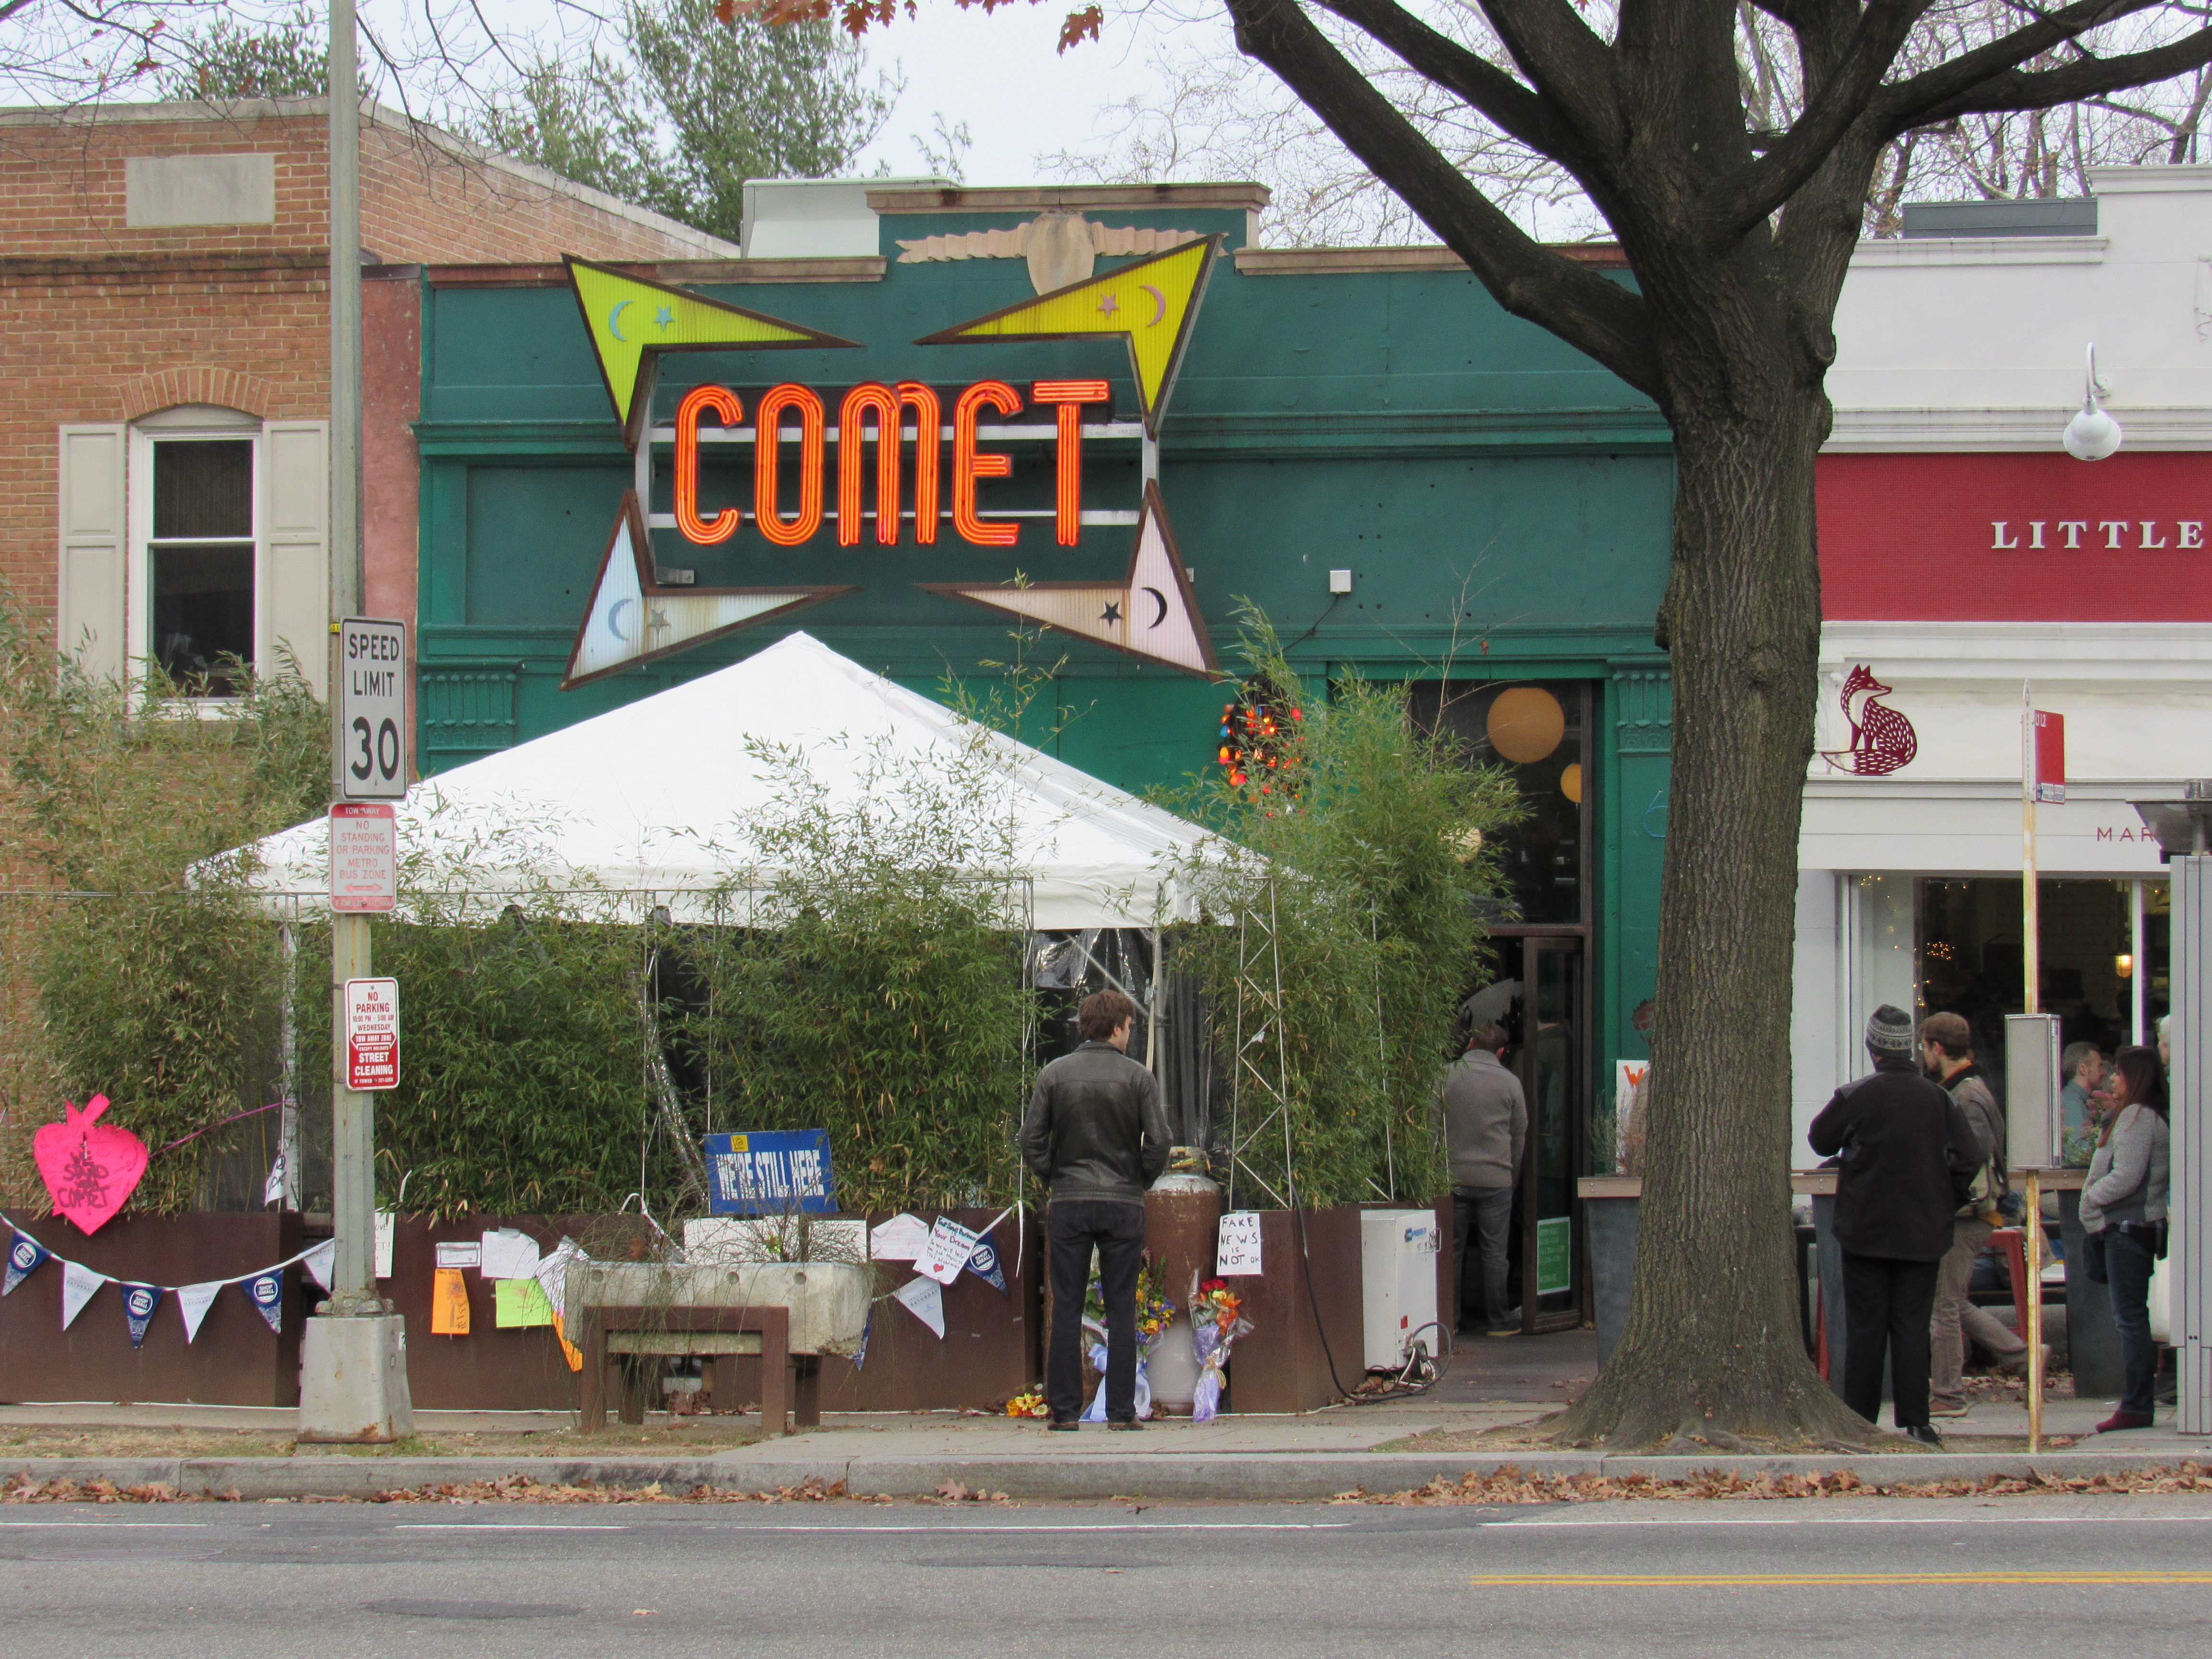
The potential consequences are just too high.  The well-cited story of the 2016 shooting up of the Comet Ping Ping pizzeria by a 28-year-old North Carolina man who was “self-investigating” a bogus news story about Hillary Clinton running a child sex abuse ring out of the location, is an excellent example of the real dangers of fake news.

More recently and closer to home, images of a woman’s body being cut open allegedly as part of a local organ theft ring were circulated widely via WhatsApp leading to wild conspiracy theories and fear.  As it turns out, the video was taken from a 2014 autopsy video causing much distress to the young lady’s family.  

Let us not be a party to these kinds of atrocities.  Let’s spot and stop fake news!


Read Past the Headline

Headlines, by their very nature, are designed to draw us in.  So too, the first paragraph is written to entice us to read further.  If we stop there, we may not have the information necessary to effectively analyse the article.  Often the body has little or nothing to do with the headline, has a disclaimer, has poor grammar indicating the information is not credible or has obvious clues the story is false.

Confirm Source, Date and Time

Some fake news sites try to fool us into believing the site is legitimate with official-sounding titles, copy cat URLs and look-alike pages.  Check the source of the material very carefully.  Take a moment to read the “About Us”.  If the language is over the top, absent or poorly written, then the source is possibly not credible.

Take a good look at the dateline of the story and other date references.  Some fake news stories and old stories or old content which have been regurgitated to appear “new”.

Questions Links, Sources, Quotes and Photos

Real journalists include citations, attribution and relevant images to enhance their stories.  Fake news writers avoid citations; they don’t have credible sources, and they steal and reuse unrelated pictures to make their points.  Be on the watch for these indicators.

Links to reference material litter real news stories.  Follow the links used to support a story and make an evaluation if they are relevant.  Look closely at the sources quoted, if any, in a story.  Do a quick internet search of their name and title to determine if they have the requisite authority to make the statement or if their quote (or a similar quote) appears on trustworthy news sites.  Finally, be sure that the image is related to the story and not just a picture transplanted from another place and time on the web page.  Google offers a reverse image search to inform if the picture has been used elsewhere on the internet.

Determine Bias

Lots of websites have declared biases; some do not.  But we need to know what we are dealing with.  Peruse the site a news story appears on to see if there is an agenda they seem to be promoting and then, take the information presented with a tablespoon of salt.

Seek Corroboration

Before you take the first link as gospel, take a moment to find out if other news organisations are reporting the same news.  Get the facts before you spread what's false!


If ever in doubt, visit the RJR News Centre for consistently credible news.

Sources


Monday, March 14, 2016

Dare I Be Invisible?

I’ve thought about it.  Stepping off the grid and becoming completely invisible; online at least.

No identity theft.  No public shaming.  No big data marketing manipulation.  No government intrusion.  And yet still, no utopia.

Being invisible is not interchangeable with being private.  Even in this digital age, we can get up, stand up and fight for our right to privacy while still enjoying the spoils of a connected world.  Ready? Set. Fight!

Just as we would not walk down a dark alley without putting up our guard and tightening our awareness of our environment, we should not traverse the digital domain without consciously monitoring our actions.  To maintain our privacy, we must constantly analyze our browsing habits, social media interactions email practices, mobile use and our passwords to maintain our privacy.

Weak Spots

Let’s start with email.  Sure, instant message (IM) services and social media dominate cyber communications, but email is still the bedrock of the online world.  Phishing scams abound!  Be suspicious of password reset notifications (that you never initiated), requests for money or personal info and viruses as each of these can be an assault on your privacy.

Social media, by its very nature, is the antithesis of privacy.  'Social' is designed for interaction, for sharing, for connections.  Yet, this is the space we must be most vigilant in protecting our identity.  For some, it is easy to forget that chatting on the internet is like chatting with a friend at a bus stop; everyone within earshot can hear.  Even if personal data is exchanged in a Direct Message (DM) versus a feed/timeline, the data is “out there”, in a public space for the world to see if they wish.

Assuming you don’t maintain fake accounts, it is certainly important to review, tweak and update your privacy settings regularly.  Facebook, Instagram (IG), LinkedIn, Pinterest, Twitter, Swarm, Snapchat, Periscope and countless other social media sites are known to change their policy, occasionally with little notification to users.

Then, there are the competitions, promotions and third party apps which are cleverly and specifically designed to mine your data under the guise of the chance at a reward.

Firewalls, anti-virus and anti-malware software, private browsing settings, cookie and ad blockers are all tools in the arsenal against prying eyes, but like a .22 calibre bullet on a meth-head, they are limited in scope if your ISP is tracking your browsing habits.  Advanced weapons like Virtual Private Networks (VPNs), Tor browsers and IP spoofing are not for the technologically challenged.

The myriad of devices collecting, collating and processing our personal data is not limited to laptop and desktop computers.  Think smaller.  Think mobile.  Tablets and phones are arguably the greatest tracking tools ever invented.  Their prominent place in our daily lives simply increases their potency. GPS tracking and tagging, insecure apps, ridiculously simple PINs, improper disposal all threaten our personal security.

A Stitch In Time

Here is the cold hard truth.  Your privacy is your right, but rights are not absolute.  That said, there are some steps you can take to defend your rights.

These days, almost everything has a password … your laptop, tablet and mobile phone, your websites and apps, hell - even your front door!  Start with a strong, unique password.  If there is even the whisper of a hack, change it.  In fact, change it every three months just to be safe.

Then, support (never remove) the password.  Two-factor authentication (2FA) is becoming a lot more popular.  When it is available, take it.  Just be sure that you keep your mobile safe too.

Think seriously about encrypting your data … your email, your IM messages … keep the contents between you and your recipient.

And always make a backup, or three.  Yes, three.  If your data is held at ransom, if there is a physical threat or if it is lost or stolen without any discernible reason, you’ll be glad you have a physical backup, an off-site backup and a cloud backup.  And remember, the backup has got to be encrypted too.

I admit, I am addicted to the many benefits of the grid - online shopping, streaming entertainment, seamless video chats with the family overseas.  So I won’t be stepping off soon.  But, I will be stepping up my privacy protocols and you should too.

Monday, September 28, 2015

Mobile Wallet: Its All About the Trinity

You’ve heard the term mobile wallet, money money and mobile payments used interchangeably because they often refer to the same thing - ditching cash in favour to mobile phones for financial transactions.

Mobile wallet services are popular all around the world; from simple SMS based systems in Kenya, carrier supported systems in Haiti to advanced handset tied systems like Google Wallet and Apple Pay, cellphone based payment systems are gaining acceptance.

Locally, Conec is the first to market with a mobile wallet service with a range of features including bill payments and person to person payments.

Can these services be trusted?  Conec says yes!


Conec, a service of JUCCL, in partnership with global provider Mozido, combines a range of tools to offer a comprehensive security system.  The tools include:
  • a guarantee that money will not be lost if the handset is lost or stolen, because the account information including account value, is stored in the cloud
  • encrypted data stored in accordance to internationally accepted standards
  • online access to account and funds, no handset required
  • a trifecta of user based safeguards - a PIN, a personal password and a secret word to restrict access


Tech4Life airs every Wednesday morning at 8:15 AM on RJR94FM.

Wednesday, May 13, 2015

Surfing Safely

A lot is done to teach kids on how to be safe is this troubled world of ours.  Children are taught how to safely cross the road, not to talk to strangers and wear helmets when riding their bikes.

But what about when kids are online?  Beyond the family desktop or Mommy’s laptop, kids have a unprecedented number of access points to the internet.  The smartphone, the tablet and even the smart TV are all connected to the World Wide Web.

Threats abound in many forms.  Porn, violence and hate speech are all inappropriate content for young children.  The success of social media has given rise to cyber bullying and cyber baiting.  And, let’s not forget, the threat of plain overexposure.

Scary ins’t it?  But fear not.  Savvy parents can protect their children with some preparation followed by education.

Family PC
You are the administrator of your computer, not your kids.  So, set up separate, restricted user accounts for each of your children to limit the content they can access.  Take it a step further and limit how long they can use the device.  You can also consider installing a monitoring app that reports on all your child’s activity online.

Installing and updating a good anti-virus software is par for the course.  Don’t forget to limit pop ups and require a password to install applications.

Mobile Device
Sadly, most smartphones and tablets do not allow for multi-user log ins.  But, that doesn’t mean that restrictions can be implemented.

All mobile devices should require a password for access; this ensures that you know when your child is using the smartphone or tablet.  

By extension, adjust the setting on your device to require a password to install apps even if they are free.  This should prevent kids from loading apps that may be inappropriate.  iPhones and iPads even offer a feature called Guided Access that can lock children into a specific app so they can't just go scrolling through your handset.

For many, phones and tablets are used for content consumption.  Fussy children get less fussy when watching their favorite video, almost like a digital pacifier.  But when the video finishes and bored kids look for the next thing to watch, make sure that you have already configured the settings to restrict any content rated PG13 or higher.

Keep your location, and your child’s location, private by disabling the GPS tracking setting.  Most devices, by default, include the location data of where pictures and videos are taken embedded in the file.  Nefarious characters can extract that information to build a profile of your activities.  

Smart TVs
Just as the digital cable box allows you to set several restrictions with a PIN to control use of the TV, smart TV’s also have built in parental controls.  Use them.

Education
The best defense against internet threats is education.  Make sure you talk to your children and let them know to:

* never give out personal information online
* never post pictures or video without permission
* never bully others online
* always report rude or suspicious activity

Educate yourself too by sharing experiences with other parents, caregivers and teachers.  Just as you would supervise your child when playing sports, so too must you supervise their activity online.

Children need to be free to explore and learn, within limits designed to keep them safe online.


Sunday, February 15, 2015

T4L - New Age Protection

I am updating my being safe online tips.  After all, it is a new year and there are new threats out there.  What worked last year simply may not be enough for 2015.  So here goes; make some time to not only read but action these safety steps.


Step 1: Back up, run anti-virus, back up again
Do it now, do it again and again.  Only the first back up is hard, each subsequent back up is incremental and therefore doesn’t take much time.  Backing up is your first and best defense against data loss which can happen for more reasons than I have space to mention.  Many systems can automate the process to an external drive or cloud service, so your only excuse is .. none.

Make sure that you download, install, run and update a good anti-malware programme, even for your mobile device.  Get rid of or prevent viruses, adware, spyware and other wares designed to destroy your life.

Step 2: Set Strong Unique Passwords
Passwords can be a pain, but they are also your first line of defense against attacks.  Forget the old rules, passwords now need to be longer than eight characters, need not be a recognizable word and need to be unique for each account.  Yes, you read that right - each account.  Since remembering scores of complicated passwords would be too much, it is time to breakout a good password manager to keep things in check.

Step 3: Secure Everything
It can be tempting to jump on a free WiFi hotspot, skip the hassle of configuring a firewall or browsing quickly through unsecured websites, but try to remember how temptation worked out for Eve.

Take a moment to set up a new password on your home wireless router and all internet enabled devices like IP cameras.  Take a moment to set up a firewall on your ‘outer, turn off Discovery and disable file sharing, especially if you plan to log on to public WiFi.

Step 4: Avoid Scams
Certainly it is not recommended that you click on links in email, but if you do, make sure there is a little lock showing in your browser window confirming that the site is secure.

Speaking of security, secure your credit card by using a dedicated ‘online card’ issued by your bank, a one time/pre-paid card or a service like Paypal to create a safety zone around your prized plastic.

Online email services like Google, Yahoo! and Outlook all offer built in virus scanners to reduce the likelihood of nefarious downloads, but it is good to remain vigilant.

Step 5: Repeat
Yes, repeat.  Continuous protection requires continuos updating.

Here’s to a safe 2015!

Tech4Life airs every Wednesday @ 8:15am on RJR94FM

Thursday, November 7, 2013

High Speed Internet - Cloud Backup

Ideally, your computer system should have three copies: a physical backup on a external drive, a second, offsite backup and a cloud backup.


The first physical backup is extremely accessible and will be the first point of contact if files need to be restored.  However, if there is more than a system crash, but a small catastrophe such as a theft or fire, the original and the first backup in close proximity are both vulnerable.

This is why an offsite backup is also recommended.  Having a full system back up at a friends house, or other suitable location, which can be accessed if the data and main backup are destroyed is prudent.

But again, a larger catastrophe, or even something as simple as your friend being on vacation with the house keys could render you incapacitated.

Fortunately, the third cloud based backup remained immediately accessible at all times.

In its simplest form, backing up to the cloud simply means saving files online; this could be a complete backup or a backup of select files.  It should also include the backup of other devices, their data and their settings.  Devices like smartphones and modems, ideally, should make the backup list.

The simplest method is to email files to yourself.  Cloud based email has become more sophisticated and many services have storage tied to the account.  iCloud, Amazon Cloud Drive, Google Drive and SkyDrive all offer free online storage that can be used to backup important files up to a point.

Free storage is generally available from your Internet Service Providers (ISP) as well.

If you prefer to have your own cloud, advanced users can configure an external hard drive to be accessible over the internet at any time. Less skilled users can opt for a pre-programmed, pre-packaged personal cloud option like pogoplug.

If that is still too much for you, paid services like Dropbox and Carbonite can work in the background to ensure you, and your data, are covered.

When deciding on which option is best, nothing beats a free trial.  Assess the option based on several factors including security and encryption policies, accessibility, scalability of space and multipoint syncing.

The first backup can take several hours and even days.  Even the subsequent, incremental backups can take time.  Especially without the benefit of a reliable, high speed internet connection.  Ultimately however, cloud backup offers the most reliable, cost effective option to ensure full data recovery.

RJR's Tech4Life airs every Wednesday at 8:15 am.